
Transform CX with AI at the core of every interaction
Unify fragmented interactions across 30+ voice, social and digital channels with an AI-native customer experience platform. Deliver consistent, extraordinary brand experiences at scale.


Contact Center Security: Threats, Best Practices & Compliance (2026)
Key Takeaways
- Contact centers hold financial and personal data, making them a prime target where a single breach carries steep cost and reputational fallout.
- The top threats now span social engineering, AI voice fraud and deepfakes, account takeover, insider risk, TDoS, and shadow AI.
- Strong security layers multiple controls: MFA and voice biometrics, encryption, role-based access, data masking, monitoring, and agent training.
- Compliance with PCI DSS, HIPAA, GDPR, CCPA/CPRA, SOC 2, and ISO 27001 sets the baseline for protecting customer data.
Contact center security is the set of protocols, technologies, and controls that protect customer data and communications across every channel a contact center handles, including voice, chat, email, SMS, and social, from breaches, fraud, and unauthorized access. Because contact centers routinely handle payment details, account credentials, and other personal data, they are among the most targeted environments in any enterprise, which makes a layered approach to security essential rather than optional.
Your contact center holds a wealth of sensitive customer information, from purchase histories and phone numbers to, in some cases, Social Security numbers.
If a cybercriminal breaches that data, it’s hard to contain that damage. An upset customer takes to X (formerly Twitter) to share their experience and your brand faces the brunt of the reputational damage while your PR and social teams scramble to respond. You risk exposing your finances just as steeply. In fact, according to a 2025 report, the global average cost of a breach sits at $4.44 million and in the United States the average is reported to be at $10.22 million.
Given the large amounts of customer data they manage, contact centers are frequent targets for cybercriminals, making strong contact center security a necessity.
That’s why ensuring robust contact center security and following best practices to protect sensitive data has never been more critical.
What is contact center security?
Contact center security safeguards the data and communications that flow through your contact center. It encompasses a comprehensive set of protocols, measures and technologies designed to protect customer information from unauthorized access, data breaches and cyber threats.
It is worth separating two terms that often get used interchangeably. Call center security traditionally refers to protecting voice interactions alone, while contact center security is broader, covering voice alongside email, SMS, live chat, and social channels. As customer conversations have moved across more channels, the security perimeter has widened with them, and so has the range of tactics attackers use to get in.
Why contact center security matters
$44.5 billion. That's the fraud exposure Pindrop's Voice Intelligence & Security Report pins on contact centers in 2025 alone. Most of it is riding on AI-synthesized voices that legacy authentication simply cannot hear as fake. Threats to contact center security are compounding.
And the paradox sitting underneath it all is that the very AI sharpening your service metrics is also the AI an attacker can turn into a weapon the moment your controls lag behind your ambition. IBM's 2025 data shows global breach costs dipped for the first time in five years. While AI-assisted detection is genuinely helping teams smother incidents faster, the same report flags that organizations bolting on AI without governance are cracking open fresh vulnerabilities. Faster containment on one side. Newer vulnerability on the other. Both true simultaneously.
What this means in practice is that a breach no longer stays inside the IT budget. It bleeds into whether a customer ever calls you again, into regulators drafting fines, into class-action filings landing on your legal team's desk. In a contact center specifically, the wound is deeper because the data being handled is rarely abstract. It’s financial and identifiable, like a Social Security number, a card-on-file, or a voiceprint. Any of it under exposure is an identity-theft nightmare for the customers who will remember your brand when it happens.
So, for contact center leaders, security is effectively tied to customer experience if the controls they enforce as weak.
Top contact center security threats you must address
Maintaining the security of your contact center requires an understanding of the cybersecurity threats that could target your organization. The following are the most pressing risks in 2026, along with how each one works.:
1. Social engineering and phishing
Social engineering attacks exploit human psychology rather than technical flaws, which is what makes them so effective. These tactics manipulate individuals into revealing sensitive information like financial details or login credentials.
One prevalent social engineering method is phishing, where cybercriminals use deceptive emails or messages that appear to be from trusted sources to trick employees into revealing sensitive information or clicking on malicious links. In a business email compromise (BEC) attack, a hacker might pose as a company executive to gain unauthorized access. This can lead to unauthorized access to your customer data. Approximately 3.4 billion malicious emails are sent daily, establishing social engineering as a primary driver of cyberattacks.
Such an event can lead to a significant loss of customer trust, as clients may begin to doubt the security of their data with your business. Beyond reputational damage, the financial and legal consequences can also include fines, legal action, and the cost of remediation.
2. AI voice fraud and deepfake scams
In the past, creating convincing deepfake audio required extensive voice recordings. But with generative AI, the process has become alarmingly quick and easy. Cybercriminals now use this technology to impersonate customers and executives, tricking contact center agents into resetting credentials or authorizing transactions. This deceptive nature of deepfake technology calls for heightened vigilance and verification in communication.
For instance, an employee in a multinational company in Hong Kong recently received a call he believed was from his company's CFO, instructing him to transfer $25.6 million. Only after the transfer did he realize a deepfake heist had deceived him.
🔧 How to tackle deepfake challenges
Start with contact center training. A well-informed team is your first defense against threats like deepfake technology. Teach them how synthetic voice and phishing attempts show up during calls, and give them clear escalation routes. Regularly training employees to recognize phishing attempts and deepfake scams during calls ensures they can find and report suspicious activity directly. It’s also essential to reinforce that any high-risk request should be verified on a second trusted channel before action is taken.
3. Account takeover and vishing
Account takeover happens when an attacker uses stolen or socially engineered credentials to seize control of a customer account, and it often runs through the contact center precisely because voice channels are harder to authenticate than digital ones. Voice phishing, or vishing, is the usual entry point: the attacker calls posing as the customer, uses breached personal data to clear knowledge-based verification, and persuades an agent to reset access. Because these calls exploit an agent’s willingness to help, they slip past many technical controls entirely, which is why authentication that does not rely on shared secrets has become essential.
4. Insider threats
Insider threats involve malicious actions or negligence by employees, contractors or other internal personnel who access the organization's systems and data. These can range from intentional data theft to accidental data exposure. Insider threats are particularly dangerous because they come from trusted individuals with legitimate access to sensitive information.
5. Telephony denial-of-service (TDoS) attacks
A telephony denial-of-service attack floods your voice lines with a high volume of malicious calls, overwhelming agents and blocking legitimate customers from getting through. Beyond the immediate disruption, TDoS is sometimes used as a smokescreen, tying up your team while an attempt at committing contact center fraud runs in parallel. Contact centers that depend on voice availability for revenue or critical support are especially exposed.
6. Third-party and shadow-AI risk
Modern contact centers run on a web of integrations, from CRM platforms to AI assistants, and each connection widens the attack surface. A growing concern is shadow AI, where agents or teams adopt unsanctioned AI tools that route customer data through systems no one has vetted. IBM’s 2025 research points to ungoverned AI as an emerging source of breaches, which makes vendor vetting and clear AI-usage policies a core part of contact center security rather than an afterthought.
Contact center security best practices
Securing your contact center is an ongoing discipline rather than a one-time project. The practices below work as layers, so that a failure in any single control does not expose the whole operation.
1. Assess security infrastructure
The first step to fortifying your contact center is assessing your existing contact center technology. Start by identifying the assets, resources and data that need protection. These could include customer information, transaction records and communication logs. You cannot secure what you have not mapped, so a clear inventory of sensitive assets is the foundation for every control that follows.
Strengthen authentication with MFA and voice biometrics
Passwords and knowledge-based questions are no longer enough on their own, because the personal details behind them are often already circulating on the dark web. Multifactor authentication raises the bar by requiring more than one form of proof, combining something the caller knows, something they have, and something they are. In the voice channel specifically, voice biometrics can verify a caller against an enrolled voiceprint in the background, and pairing it with liveness detection helps flag synthetic or replayed audio before an agent ever acts on the request.
Assign role-based access control
One of the most effective ways to secure sensitive information is through role-based access control. This method limits access to data and resources based on your employee’s role. For instance, customer service representatives may access customer information, not financial records or internal communications. This reduces the risk of unauthorized entry and potential data breaches.
💡 Pro Tip: Leverage your contact center software to limit who can access sensitive information. Sprinklr Service runs on a role-based access control model, so you decide exactly what each person can see and do. Through roles, user groups, and granular permissions in the Governance module, you can give every agent access to only the areas they need and nothing more, which keeps sensitive customer data out of the wrong hands and lowers the odds of accidental exposure. That's backed up at the platform level by safeguards like optional two-factor authentication and encrypted data that no end user can reach directly. It also helps to keep sensitive details off live channels in the first place: Sprinklr's customer self-service tools, from AI agents and voice bots, let customers handle routine requests on their own, so fewer personal details ever pass through a live agent.
Encrypt your data
Encryption is a powerful tool for protecting your data from cyberattacks. When encrypted, data is converted into a code that can only be deciphered by someone with the correct encryption key. There are two types of encryption: encryption at rest and encryption in transit. Encryption at rest protects data stored on your servers or databases. In contrast, encryption in transit protects data as it moves across networks, such as during email communication or file transfers.
Mask sensitive data and secure call recordings
Even authorized agents rarely need to see a full card number or government ID to do their job. Data masking hides these details from view while still letting agents work, which reduces the chance of exposure through a compromised account or a screen capture. The same care applies to call recordings and transcripts, which often contain sensitive information and should be encrypted, access-controlled, and retained only as long as compliance requires.
🤺 How Sprinklr combats data breaches
Sprinklr prioritizes protecting customer data and staying one step ahead of potential threats. For example, Sprinklr’s live chat support software is designed with robust security features that add multiple layers of protection, ensuring your customer interactions remain secure and confidential. Here’s how:
Single sign-on (SSO): You can streamline and secure user authentication by allowing customers to access multiple services with a single set of login credentials. This reduces the risk of password fatigue and minimizes the potential for unauthorized access.
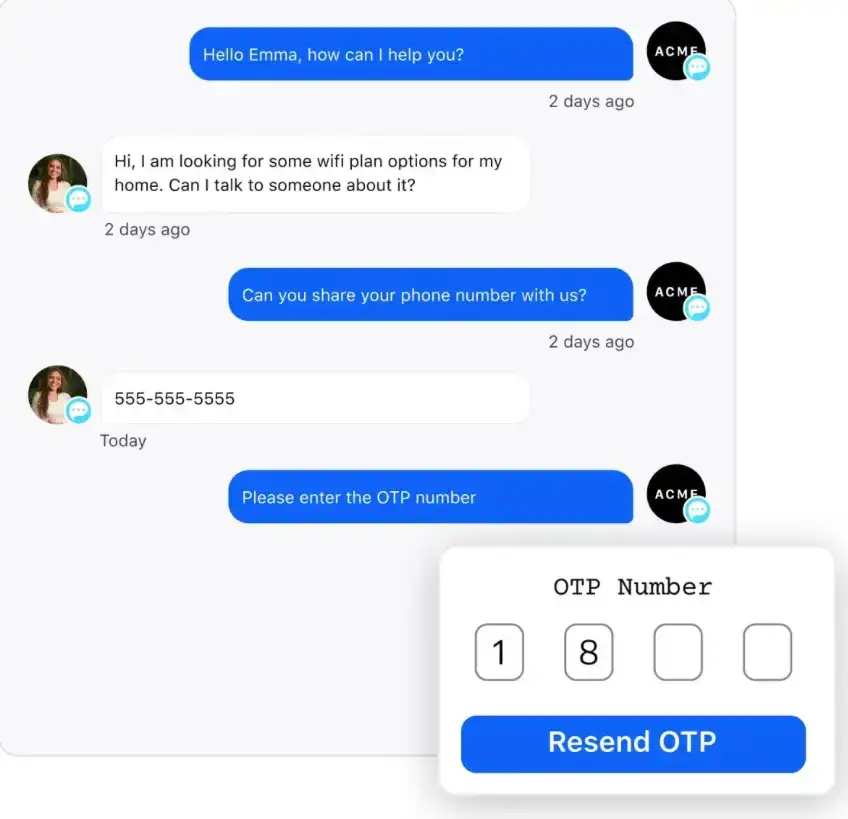
OTP validations: One-time password (OTP) validations enhance security, ensuring that only verified users can access sensitive information during chat sessions.
Secure chat links: Generate secure chat links that encrypt conversations end-to-end, protecting the data as it travels between the user’s device and your contact center.
Secure handshakes: Implement secure handshakes between your website, app and chat interface, ensuring that data is transmitted safely and only to intended recipients.
Implement continuous monitoring
Continuous monitoring is essential for maintaining a high level of security in your contact center. Automated monitoring systems can constantly monitor your network, identifying and alerting you to potential threats in real time. These systems are designed to detect unusual activities, such as a sudden spike in login attempts, unfamiliar bots or anomalies in data usage patterns.
Train your agents
Your agents are both your first line of defense and a frequent target, so security training cannot be a one-time onboarding exercise. Regular, scenario-based training on phishing, vishing, and deepfake tactics helps agents recognize and report suspicious activity in the moment, and a clear verification protocol gives them a safe way to slow down a high-pressure request without hurting the customer experience.
Compliance standards for contact centers
Strong security and regulatory compliance reinforce each other, and for most contact centers a handful of frameworks set the baseline. Which ones apply depends on your industry and the regions you serve, but these are the most common:
- PCI DSS governs how card payment data is handled and applies to any contact center that processes transactions.
- HIPAA sets the standard for protecting health information in the United States and applies to healthcare organizations and their partners.
- GDPR governs the personal data of individuals in the European Union and carries some of the steepest penalties for non-compliance.
- CCPA and CPRA extend similar privacy protections to California residents and increasingly serve as a model for other US states.
- SOC 2 Type II and ISO/IEC 27001 are voluntary certifications that demonstrate a mature, independently audited security program, and enterprise buyers often expect them from vendors.
Meeting these standards is not a one-time exercise. It calls for continuous auditing, clear data-handling policies, and evidence that controls are working as intended. For a deeper walkthrough, see our guide to contact center compliance.
Contact center security trends to watch in 2026
Several key trends are emerging in 2025 that will shape the landscape of contact center security. Understanding and integrating these trends will be crucial for businesses to avoid potential threats and safeguard sensitive customer data.
1. AI-based threat detection
With AI-based threat detection, your contact center can identify real-time risks and initiate action. The technology doesn’t just react to threats—it predicts them by analyzing patterns and identifying anomalies. The systems use machine learning algorithms to detect unusual patterns in network traffic, user behavior and system logs, flagging potential security breaches before they cause harm.
2. Zero trust architecture
The traditional approach of trusting everything within a network perimeter is now obsolete. In 2026, Zero Trust Architecture (ZTA) is becoming a standard security framework for contact centers. ZTA operates on the principle of "never trust, always verify," ensuring that every user, device and connection is authenticated and authorized before access is granted. This trend is driven by the increasing complexity of hybrid work environments, where employees may access contact center systems from various locations and devices.
3. AI agents must be protected from prompt injections
As AI agents go from simply answering questions to doing things, like updating accounts or pulling up records, they become something you have to secure in their own right. Anything they read, from a document to a chat message, can hide sneaky instructions that trick them into misbehaving.
It's a problem called prompt injection, and there's still no clean way to do away with it. Since customer service is where these agents are taking off fastest, frameworks such as the NIST AI Risk Management Framework and the OWASP LLM Top 10 are becoming the reference points for governing agents with human approval for sensitive actions and continuous monitoring.
4. Security built into customer experience
Security and customer experience are no longer separate domains. The greater focus today is on integrating cybersecurity measures seamlessly with customer interactions. This includes ensuring that security protocols do not disrupt the but instead enhance it, such as using secure, encrypted customer communication channels or implementing customer-friendly, low-friction authentication processes that balance security with convenience.
How Sprinklr secures your contact center
For many enterprises, keeping up with modern security threats while staying focused on core contact center business objectives is daunting. The pressure to safeguard sensitive customer data can be overwhelming, often stretching your team thin and leaving your business vulnerable to potential breaches.
This is where Sprinklr Service steps in. With comprehensive insights and a unified platform built to stay ahead of evolving threats. The exhaustive security measures, from state-of-the-art encryption to proactive threat monitoring, are designed to handle the complexities of today’s cybersecurity challenges.
Built on the Unified-CXM platform, trusting Sprinklr means your contact center is secured using enterprise-grade encryption, role-based access, and proactive monitoring together in one place, so security is part of the platform rather than a set of tools bolted on afterward.
Frequently Asked Questions
Contact center security is the combination of protocols, technologies, and controls that protect customer data and communications across voice, chat, email, SMS, and social channels from breaches, fraud, and unauthorized access.
Call center security focuses on voice interactions, while contact center security covers every channel, including voice, email, SMS, live chat, and social, reflecting how modern omnichannel operations actually work.
The leading threats are social engineering and phishing, AI-powered voice fraud and deepfakes, account takeover via vishing, insider threats, and telephony denial-of-service (TDoS) attacks.
Layer multifactor and biometric authentication, encrypt data in transit and at rest, enforce role-based access, mask sensitive data, monitor continuously for anomalies, and train agents to spot social-engineering and deepfake attempts.
Common frameworks include PCI DSS for payment data, HIPAA for healthcare, GDPR and CCPA/CPRA for privacy, and SOC 2 Type II and ISO/IEC 27001 for security governance.

